
Oracle Fusion Cloud Applications protect customer data through built-in controls. For eligible customers needing additional control over exceptional Oracle administrative access, Oracle Managed Access is the access-governance component of Oracle Break Glass. Within the applicable Break Glass coverage, it provides a customer-configurable process for exceptional, temporary administrative access by authorized Oracle personnel when legitimate service-related intervention is required.
Oracle Managed Access does not provide unrestricted administrative access. It aligns access with the entitlement required for the approved activity. Any permitted access to customer data is strictly read-only, while administrative entitlements support service operations without granting access to customer data.
A Governed, Time-Bound Access Workflow
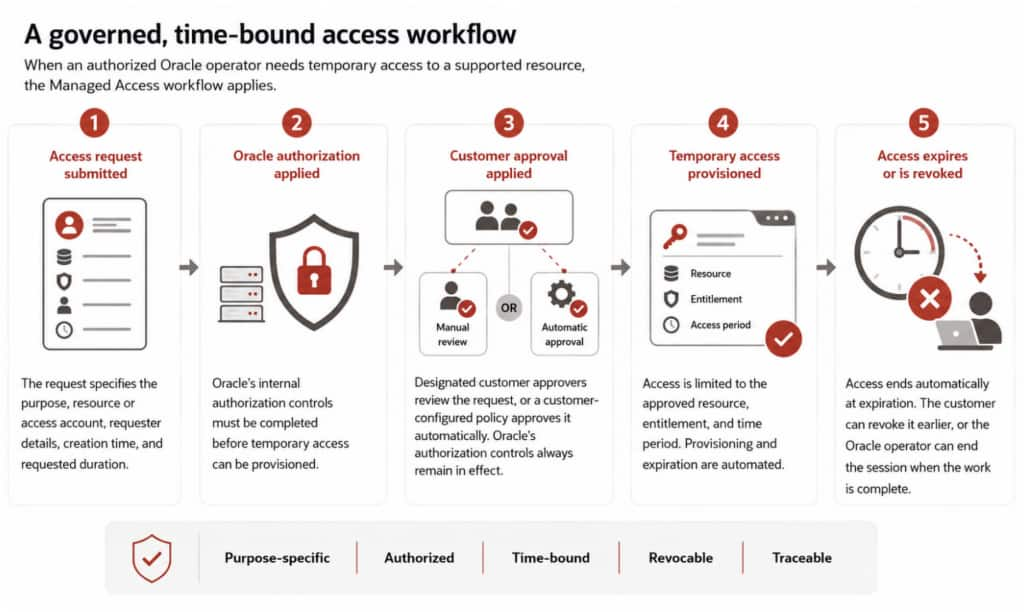
When an authorized Oracle operator requires temporary access to a supported resource, the Managed Access workflow applies:
- The Oracle operator submits an access request. It identifies the purpose, resource or access account, requester’s identifier and location, and requested duration.
- Oracle’s authorization controls are applied. The request follows Oracle’s internal authorization process before temporary access can be provisioned.
- The customer-defined approval policy is applied. The customer policy can require designated approvers or a customer-configured automatic approval step. Automatic approval applies only to the customer step; Oracle’s internal authorization controls continue to apply.
- Temporary access is provisioned. After authorization and approval, the operator receives the approved entitlement for the approved resource and period. Provisioning and expiration are automated.
- Access expires or is revoked. Access ends when the authorized period expires, and applicable active sessions are terminated. A customer can revoke access earlier, and the operator can end the session sooner.
This process makes exceptional Oracle administrative access purpose-specific, authorized, time-bound, revocable, and traceable.
Customer-Defined Approval Policies
Customers can configure Managed Access approval policies to identify designated approvers, determine whether the customer approval step is manual or automatic, and set the permitted duration of temporary access. Oracle Break Glass supports access periods ranging to a maximum of 96 hours.
Under a manual policy, designated approvers are notified when a request is ready for review and can approve, decline, or revoke it.
An automatic policy removes the need for a case-by-case customer decision, but not Oracle’s internal authorization controls or the resulting time limit. Customers using manual approval should establish clear responsibilities, urgent-request coverage, and escalation procedures. Delayed approval may affect Oracle’s ability to perform support, maintenance, or change-management activities within the intended timeframe.
Access Aligned With the Approved Service Activity
Managed Access uses entitlement types to align access with the service-related activity being performed:
- Support Team Entitlements provide strictly read-only access to customer content residing in the Fusion database, enabling authorized Oracle personnel to triage service requests logged in My Oracle Support.
- Database Administrator Entitlements support approved database-related activities, such as patching, upgrading, troubleshooting, and backup restoration, without providing access to customer data.
- Application or Mid-Tier Administrator Entitlements support approved application- and middleware-related activities without customer-data access.
In every case, access is tied to a specific request, applicable entitlement, and approved period.
Individual Accountability and Timely Access Decisions
When more than one Oracle operator needs concurrent access to the same supported resource, each submits a separate request that follows the workflow independently, preserving individual accountability and traceability.
When a manually approved request remains pending, the requesting operator can send limited reminders to designated approvers. An operator can cancel only the request that they initiated.
Visibility Into Requests and Access History
Managed Access gives customers visibility into exceptional Oracle administrative access requests and their status. Available information may include the request name and identifier, business rationale and related service request, secured resource and access account, requester’s identifier and country location, request state and duration, and relevant creation, update, approval, and expiration times.
Customers can review current and historical requests and obtain an access report for a selected period. For supported implementations, the information can be exported for further analysis and use in internal governance or compliance processes.
Reporting provides high-level, timestamped access-event traceability; it does not provide a detailed record of individual commands, operations, or specific customer data viewed, changed, or otherwise accessed by Oracle personnel.
Customer Control for Exceptional Access
Oracle Managed Access gives eligible customers a way to govern exceptional, time-bound Oracle administrative access needed to support their Fusion environment. It adds customer control to Oracle’s established service practices without replacing the data-protection controls built into Oracle Fusion Cloud Applications. The next article examines Bring Your Own Key (BYOK) and the customer responsibilities involved in governing the TDE master encryption key used to protect the Fusion database.