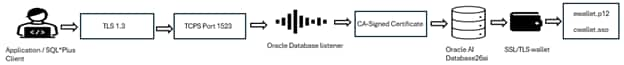
To ensure secure communication among Oracle Globally Distributed AI Database components in a distributed environment, Oracle recommends using Oracle Database Native Network Encryption or the TCP/IP with Transport Layer Security (TCPS) protocol to encrypt and protect all connections to and between the shard catalog and individual shards.
This procedure explains how to configure TLS 1.3 over TCPS in Oracle AI Database 26ai using a certificate issued by a third-party Certificate Authority (CA), such as DigiCert, Sectigo, GlobalSign, or an enterprise PKI.
Step 1: Verify database version
Step 2: Verify DB and default listener must be up and running.
Step 3: Create the wallet directory
Log in as the Oracle software owner.
su – oracle
Create SSL wallet directory and set the permissions:
mkdir -p /refresh/home/tls_wallet
chmod 700 /refresh/home/tls_wallet
Step 3: Create the Oracle Wallet
orapki wallet create -wallet <<wallet_path>> -pwd <<wallet_password>> -auto_login
[oracle@linux9 ~]$ mkdir -p /refresh/home/tls_wallet
[oracle@linux9 ~]$
[oracle@linux9 ~]$ orapki wallet create -wallet /refresh/home/tls_wallet -pwd Oracle_1234 -auto_login
Oracle PKI Tool Release 23.0.0.0.0 – Production
Version 23.0.0.0.0
Copyright (c) 2004, 2025, Oracle and/or its affiliates. All rights reserved.
Operation is successfully completed.
[oracle@linux9 ~]$
[oracle@linux9 ~]$ ls -ltr /refresh/home/tls_wallet
total 8
-rw——- 1 oracle oracle 0 Nov 3 18:28 ewallet.p12.lck
-rw——- 1 oracle oracle 225 Nov 3 18:28 ewallet.p12
-rw——- 1 oracle oracle 0 Nov 3 18:28 cwallet.sso.lck
-rw——- 1 oracle oracle 270 Nov 3 18:28 cwallet.sso
[oracle@linux9 ~]$
Step 4: Generate a Private Key and Certificate Signing Request (CSR)
A CSR is submitted to the third-party CA, which verifies the requested identity and issues a signed certificate
orapki wallet add -wallet /refresh/home/tls_wallet -dn “CN=db26ai.vm.oracle.com,O=MyCompany,C=US” -keysize 2048
[oracle@db26ai ssl_wallet]$ orapki wallet add -wallet /refresh/home/tls_wallet -dn “CN=db26ai.vm.oracle.com,O=MyCompany,C=US” -keysize 2048
Oracle PKI Tool Release 23.0.0.0.0 – Production
Version 23.0.0.0.0
Copyright (c) 2004, 2025, Oracle and/or its affiliates. All rights reserved.
Cannot modify auto-login (sso) wallet
Enter wallet password:
Operation is successfully completed.
[oracle@db26ai ssl_wallet]$
This generates the private key and certificate request associated with the specified DN. The private key remains in the Oracle Wallet.
Step 5: Export the CSR
orapki wallet export -wallet /refresh/home/tls_wallet -dn “CN=db26ai.vm.oracle.com,O=MyCompany,C=US” -request “/tmp/db26ai.csr”
[oracle@db26ai ssl_wallet]$ orapki wallet export -wallet /refresh/home/tls_wallet -dn “CN=db26ai.vm.oracle.com,O=MyCompany,C=US” -request “/tmp/db26ai.csr”
Oracle PKI Tool Release 23.0.0.0.0 – Production
Version 23.0.0.0.0
Copyright (c) 2004, 2025, Oracle and/or its affiliates. All rights reserved.
Operation is successfully completed.
[oracle@db26ai ssl_wallet]$
[oracle@db26ai ssl_wallet]$ ls -ltr /tmp/db26ai.csr
-rw——- 1 oracle oracle 959 Nov 4 18:22 /tmp/db26ai.csr
[oracle@db26ai ssl_wallet]$
Inspect the CSR:
openssl req -in /tmp/db26ai.csr -noout -text
Verify the subject and public key. Certificate SAN requirement: Ensure the issued certificate contains a Subject Alternative Name (SAN) covering the hostname used by database clients, such as db26ai.example.com. Confirm the CA’s SAN enrollment requirements before submitting the CSR.
Step 6: Submit the CSR to the CA Authority
Please submit the db26ai.csr file to your organization’s approved Certificate Authority (CA) and request a CA-signed server certificate. Once the certificate signing process is complete, the CA will typically provide the following three files:
db26ai.crt è SERVER CERTIFICATE
intermediateCA.crt è INTERMEDIATE CERTIFICATE
rootCA.crt è Trusted Root CA certificate
Please Note : Do not submit the wallet private key to the CA. Only submit the CSR.
Step 7: Import the root CA certificate
Copy the three certificates received from your organization’s Certificate Authority (CA) to the database server. You can either use an existing directory or create a new dedicated directory to store these certificate files.
orapki wallet add -wallet /refresh/home/tls_wallet -trusted_cert -cert /refresh/home/certificates/rootCA.crt
Step 8: Import intermediate CA certificates
orapki wallet add -wallet /refresh/home/tls_wallet -trusted_cert -cert /refresh/home/certificates/intermediateCA.crt
Sometimes CA provides multiple intermediate certificates, import all required certificates in the chain.
Step 9: Import the signed database server certificate
orapki wallet add -wallet /refresh/home/tls_wallet –user_cert -cert /refresh/home/certificates /db26ai.crt
The certificate must correspond to the private key and CSR generated in the same wallet.
Step 10: Verify the Oracle Wallet
orapki wallet display -wallet /refresh/home/tls_wallet
After importing the CA-signed server certificate, intermediate CA certificate, and root CA certificate, your Oracle Wallet should display the following certificate information:
[oracle@db26ai wallet]$ orapki wallet display -wallet .
Oracle PKI Tool Release 23.0.0.0.0 – Production
Version 23.0.0.0.0
Copyright (c) 2004, 2025, Oracle and/or its affiliates. All rights reserved.
Requested Certificates:
User Certificates:
Subject: CN=db26ai.vm.oracle.com,O=Oracle26aiLab,C=US
Trusted Certificates:
Subject: CN=Oracle26ai-Intermediate-CA,O=Oracle26aiLab,C=US
Subject: CN=Oracle26ai-Root-CA,O=Oracle26aiLab,C=US
[oracle@db26ai wallet]$
Step 11: Update listener.ora
Back up the configuration:
cp -p listener.ora listener.ora.bak
Edit:
LISTENER =
(DESCRIPTION_LIST =
(DESCRIPTION =
(ADDRESS = (PROTOCOL = TCP)(HOST = db26ai.vm.oracle.com)(PORT = 1521))
(ADDRESS = (PROTOCOL = TCPS)(HOST = db26ai.vm.oracle.com)(PORT = 1523))
(ADDRESS = (PROTOCOL = IPC)(KEY = EXTPROC1521))
)
)
ENABLE_GLOBAL_DYNAMIC_ENDPOINT_PDB_LISTENER = ON
VALID_NODE_CHECKING_REGISTRATION_PDB_LISTENER = SUBNET
WALLET_LOCATION =
(SOURCE=
(METHOD=File)
(METHOD_DATA=
(DIRECTORY=/refresh/home/tls_wallet)
)
)
SSL_CLIENT_AUTHENTICATION=FALSE
SSL_VERSION=1.3
In RAC environment If the listener runs from Grid Infrastructure, configure the appropriate Grid Infrastructure listener and wallet rather than assuming the database Oracle Home owns the listener.
Step 12: Update sqlnet.ora
Back up the file sqlnet.ora and edit.
Edit:
NAMES.DIRECTORY_PATH= (TNSNAMES, EZCONNECT)
SQLNET.AUTHENTICATION_SERVICES = (BEQ, TCPS)
WALLET_LOCATION =
(SOURCE =
(METHOD = FILE)
(METHOD_DATA =
(DIRECTORY = /refresh/home/tls_wallet)
)
)
SSL_VERSION = 1.3
SSL_CLIENT_AUTHENTICATION = FALSE
Step 13: Restart the Oracle Listener and database
Step 14: Add entry in tnsnames.ora
ORCL_SSL =
(DESCRIPTION =
(ADDRESS =
(PROTOCOL = TCPS)
(HOST = db26ai.vm.oracle.com)
(PORT = 1523)
)
(CONNECT_DATA =
(SERVER = DEDICATED)
(SERVICE_NAME = orcl)
)
(SECURITY =
(SSL_SERVER_DN_MATCH = YES)
(WALLET_LOCATION = /refresh/home/tls_wallet)
)
)
Step 15: Verify Local Database Connectivity Using TNSPING and SQL*Plus.
[oracle@db26ai wallet]$ tnsping ORCL_SSL
TNS Ping Utility for Linux: Version 23.26.1.0.0 – for Oracle Cloud and Engineered Systems on 04-NOV-2026 17:24:43
Copyright (c) 1997, 2025, Oracle. All rights reserved.
Used parameter files:
/refresh/home/app/oracle/product/23.26.1/network/admin/sqlnet.ora
Used TNSNAMES adapter to resolve the alias
Attempting to contact (DESCRIPTION = (ADDRESS = (PROTOCOL = TCPS) (HOST = db26ai.vm.oracle.com) (PORT = 1523)) (CONNECT_DATA = (SERVER = DEDICATED) (SERVICE_NAME = orcl)) (SECURITY = (SSL_SERVER_DN_MATCH = YES) (WALLET_LOCATION = /refresh/home/oracle26ai_ssl/client_wallet)))
OK (10 msec)
[oracle@db26ai ssl_wallet]$ sqlplus -L ‘c##tapp01@ORCL_SSL’
SQL*Plus: Release 23.26.1.0.0 – for Oracle Cloud and Engineered Systems on Wed Nov 4 20:01:41 2026
Version 23.26.1.0.0
Copyright (c) 1982, 2025, Oracle. All rights reserved.
Enter password:
Last Successful login time: Wed Nov 04 2026 17:24:48 +00:00
Connected to:
Oracle AI Database 26ai Enterprise Edition Release 23.26.1.0.0 – for Oracle Cloud and Engineered Systems
Version 23.26.1.0.0
SQL> SELECT sys_context(‘USERENV’,’NETWORK_PROTOCOL’) AS protocol FROM dual;
PROTOCOL
——————————————————————————–
tcps
SQL>
Configure the Oracle Client to Establish a Secure Database Connection Using the TCPS Port.
Step1: Login on Linux client machine and create the wallet directory
mkdir -p /home/oracle/oracle26ai_ssl/client_wallet
mkdir -p /home/oracle/oracle26ai_ssl/certs
chmod 700 /home/oracle/oracle26ai_ssl/client_wallet
chmod 700 /home/oracle/oracle26ai_ssl/certs
Step2: Copy CA Certificates to the Linux client machine
rootCA.crt
intermediateCA.crt
Step3: Create an Oracle Client Wallet
orapki wallet create -wallet /home/oracle/oracle26ai_ssl/client_wallet -auto_login
Step 4 : Import the Root CA Certificate into the Client Wallet
orapki wallet add -wallet /home/oracle/oracle26ai_ssl/client_wallet
-trusted_cert -cert /home/oracle/oracle26ai_ssl/certs/rootCA.crt
Step 5: Import the Intermediate CA Certificate
orapki wallet add -wallet /home/oracle/oracle26ai_ssl/client_wallet -trusted_cert -cert /home/oracle/oracle26ai_ssl/certs/intermediateCA.crt
Step 6: Verify the Oracle Client Wallet
Step 7: Configure sqlnet.ora on the Linux Client and Add the following configuration
NAMES.DIRECTORY_PATH = (TNSNAMES, EZCONNECT)
WALLET_LOCATION =
(SOURCE =
(METHOD = FILE)
(METHOD_DATA =
(DIRECTORY = /home/oracle/oracle26ai_ssl/client_wallet)
)
)
TLS_VERSION = 1.3
TLS_CLIENT_AUTHENTICATION = FALSE
TLS_SERVER_DN_MATCH = TRUE
Step8 : Configure tnsnames.ora on the Linux Client
CLI_SSL =
(DESCRIPTION =
(ADDRESS =
(PROTOCOL = TCPS)
(HOST = db26ai.vm.oracle.com)
(PORT = 1523)
)
(CONNECT_DATA =
(SERVER = DEDICATED)
(SERVICE_NAME = orcl)
)
(SECURITY =
(TLS_SERVER_DN_MATCH = TRUE)
(WALLET_LOCATION = /home/oracle/oracle26ai_ssl/client_wallet)
)
)
Step 8: Test tnsping and SQL*Plus Connection from the Linux Client tnsping
Tnsping CLI_SSL
Sqlplus <<app_user>>@CLI_SSL
